Taiwan Mobile Co. (TWM) established a risk management policy in 2011,
and relevant policies and procedures were disclosed on the official
website. The policy was revised for the fifth
time by the Board of Directors in 2025 as the highest
guiding principle for risk management. The
Company actively plans risk management policies, the organizational
structure and risk management systems; potential risks in the operation
of the Company are dealt with on a preventive basis before they
occur.
The Risk Management Committee was established in
2015 with the approval of the Board of Directors. In November 2025, to
enhance the level of risk management governance, the Risk Management
Committee was incorporated into the Audit and Risk Management Committee,
a functional committee under the Board of Directors, with a Risk
Management Steering Committee established under it to strengthen the
Company's risk management mechanism. The Audit and Risk Management
Committee assists the Board of Directors in overseeing and reviewing the
operation and implementation of risk management. The Risk Management
Steering Committee is responsible for coordinating risk-related matters
and implementing risk management decisions, and reports on its
operations to the Audit and Risk Management Committee and the Board of
Directors at least once a year to ensure that relevant risk issues are
effectively managed.
The Internal Audit Office conducts an annual review of the risk
management mechanism and annual year-end risk assessments, and rates the
importance and possibility of each risk, then calculates the risk value
according to the results of the rating. The risk value becomes the basis
for the following year's audit plan.
In 2025, the audit results did not show any
internal control deficiencies and abnormalities. Nevertheless,
59 concrete suggestions for improving
operational procedures were proposed as ways to improve the quality of
management. The improvements and suggestions are to be tracked on a
quarterly basis until they have been completed.
Risk Management Scope
TWM integrates and manages various important risks that may affect
operations and profits by proactive and cost-effective manner along with
a response mechanism from the three-level risk management.
The company's important risks include "Operating risk", "Risks
related to information privacy and security", "Innovation risk"... and
so on. Please read the detail content in the company's annual
report.
Risk Management Structure
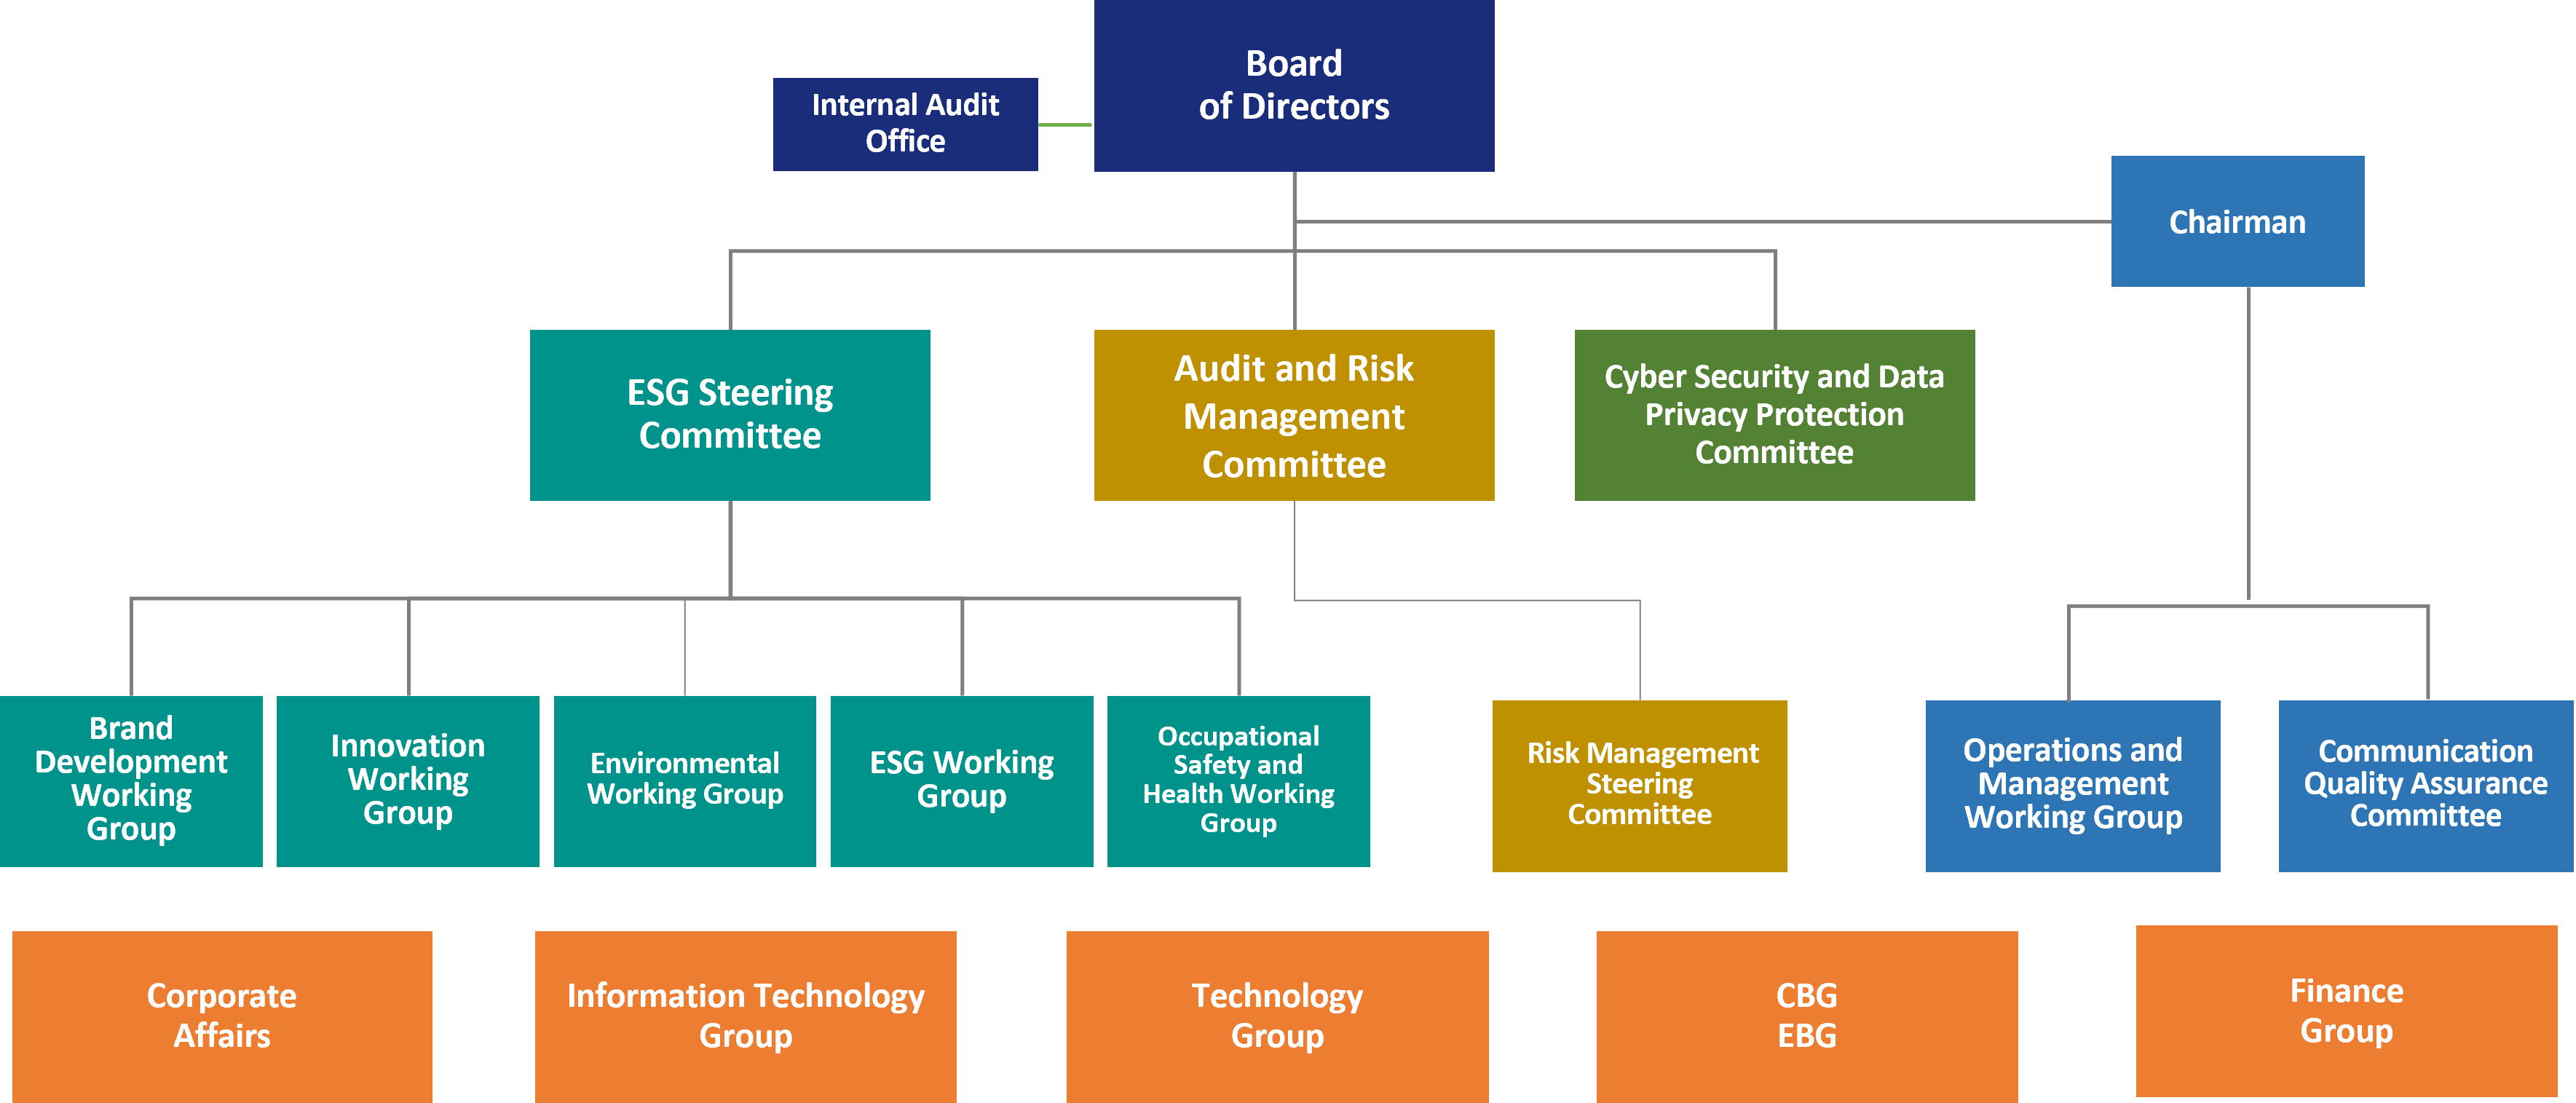
*NoteThe Board of Directors exercises control over the ESG Steering Committee and the Cyber Security and Data Privacy Protection Committee. The Audit and Risk Management Committee is a functional committee under the Board of Directors, with the Risk Management Steering Committee established under it. If any major event or incident happens, the responsible unit shall report it to the Operations and Management Committee and corresponding Committee or Working Group to undertake any necessary measures.
Risk Operation
TWM has established the Audit and Risk Management
Committee, which consists of all independent directors of the Company
and is chaired by one of the independent directors. A Risk Management
Steering Committee is established under the Audit and Risk Management
Committee to supervise and strictly control risk management-related
issues and continuously promote a risk management-oriented management
model to achieve continuous improvement.
The Risk Management Steering Committee meets at
least once every six months and regularly communicates and discusses
risk management-related issues with various committees and working
groups, including the Operations and Management Committee, Occupational
Safety and Health Committee, Communication Quality Assurance Committee,
Cyber Security and Data Privacy Protection Committee, ESG Steering
Committee, Environmental Working Group, and Innovation Working Group, to effectively identify risk issues across different
areas.
In the event of a major event or proposal, each responsible unit
shall report it to a meeting of operation management or each management
committee to decide the necessary measures. Each functional committee
not only proactively focus and identify the potential risk issues within
internal and external for the company, but bring up appropriate
solutions.
The company has proactively promoted the mechanism of risk management
since 2011.
The followings are the status of main operating over the years.
Formulated Risk Management Policy in 2011.
The Risk Management Committee was established in 2015.
Revised the Risk Management Policy in 2017.
The Risk Management Policy was revised the second time in
2020.
The Chief Internal Auditor attended the Board of Directors to
report the business of the Risk Management Committee on August 5,
2021.
The Risk Management Committee meeting was convened for second
time to discuss 17 issues in 2021.
Revised the Risk Management Policy for third time and approved by
the Board of Directors in2022.
The Chief Internal Auditor attended the Board of Directors to
report the business of the Risk Management Committee on August 1st ,
2022.
The Risk Management Committee meeting was convened for second
time to discuss 19 issues in 2022.
The Chief Internal Auditor attended the Board of Directors to
report the business of the Risk Management Committee on August 4 ,
2023.
The Risk Management Committee meeting was convened for second
time to discuss 17 issues in 2023.
The Chief Internal Auditor attended the Board of Directors to
report the business of the Risk Management Committee on August 5 ,
2024.
In 2025, the Risk Management Committee
convened meetings in May and November, with a total of 12 agenda items.
Various committees and working groups reported on risk-related issues,
including the identified risks and corresponding risk treatment
measures. The operations of the Risk Management Committee were reported
to the Board of Directors on August 7, 2025.
In 2025, the Risk Management Committee convened
meetings in May and November to discuss a total of 12 agenda items on
risk-related issues and corresponding mitigation measures proposed by
various committees and working groups. The Committee reported its
operations to the Board of Directors on August 7, 2025. In November
2025, to enhance risk management governance, the Risk Management
Committee was incorporated into the Audit and Risk Management Committee,
with the Risk Management Steering Committee established under
it.
Risk Management Procedure
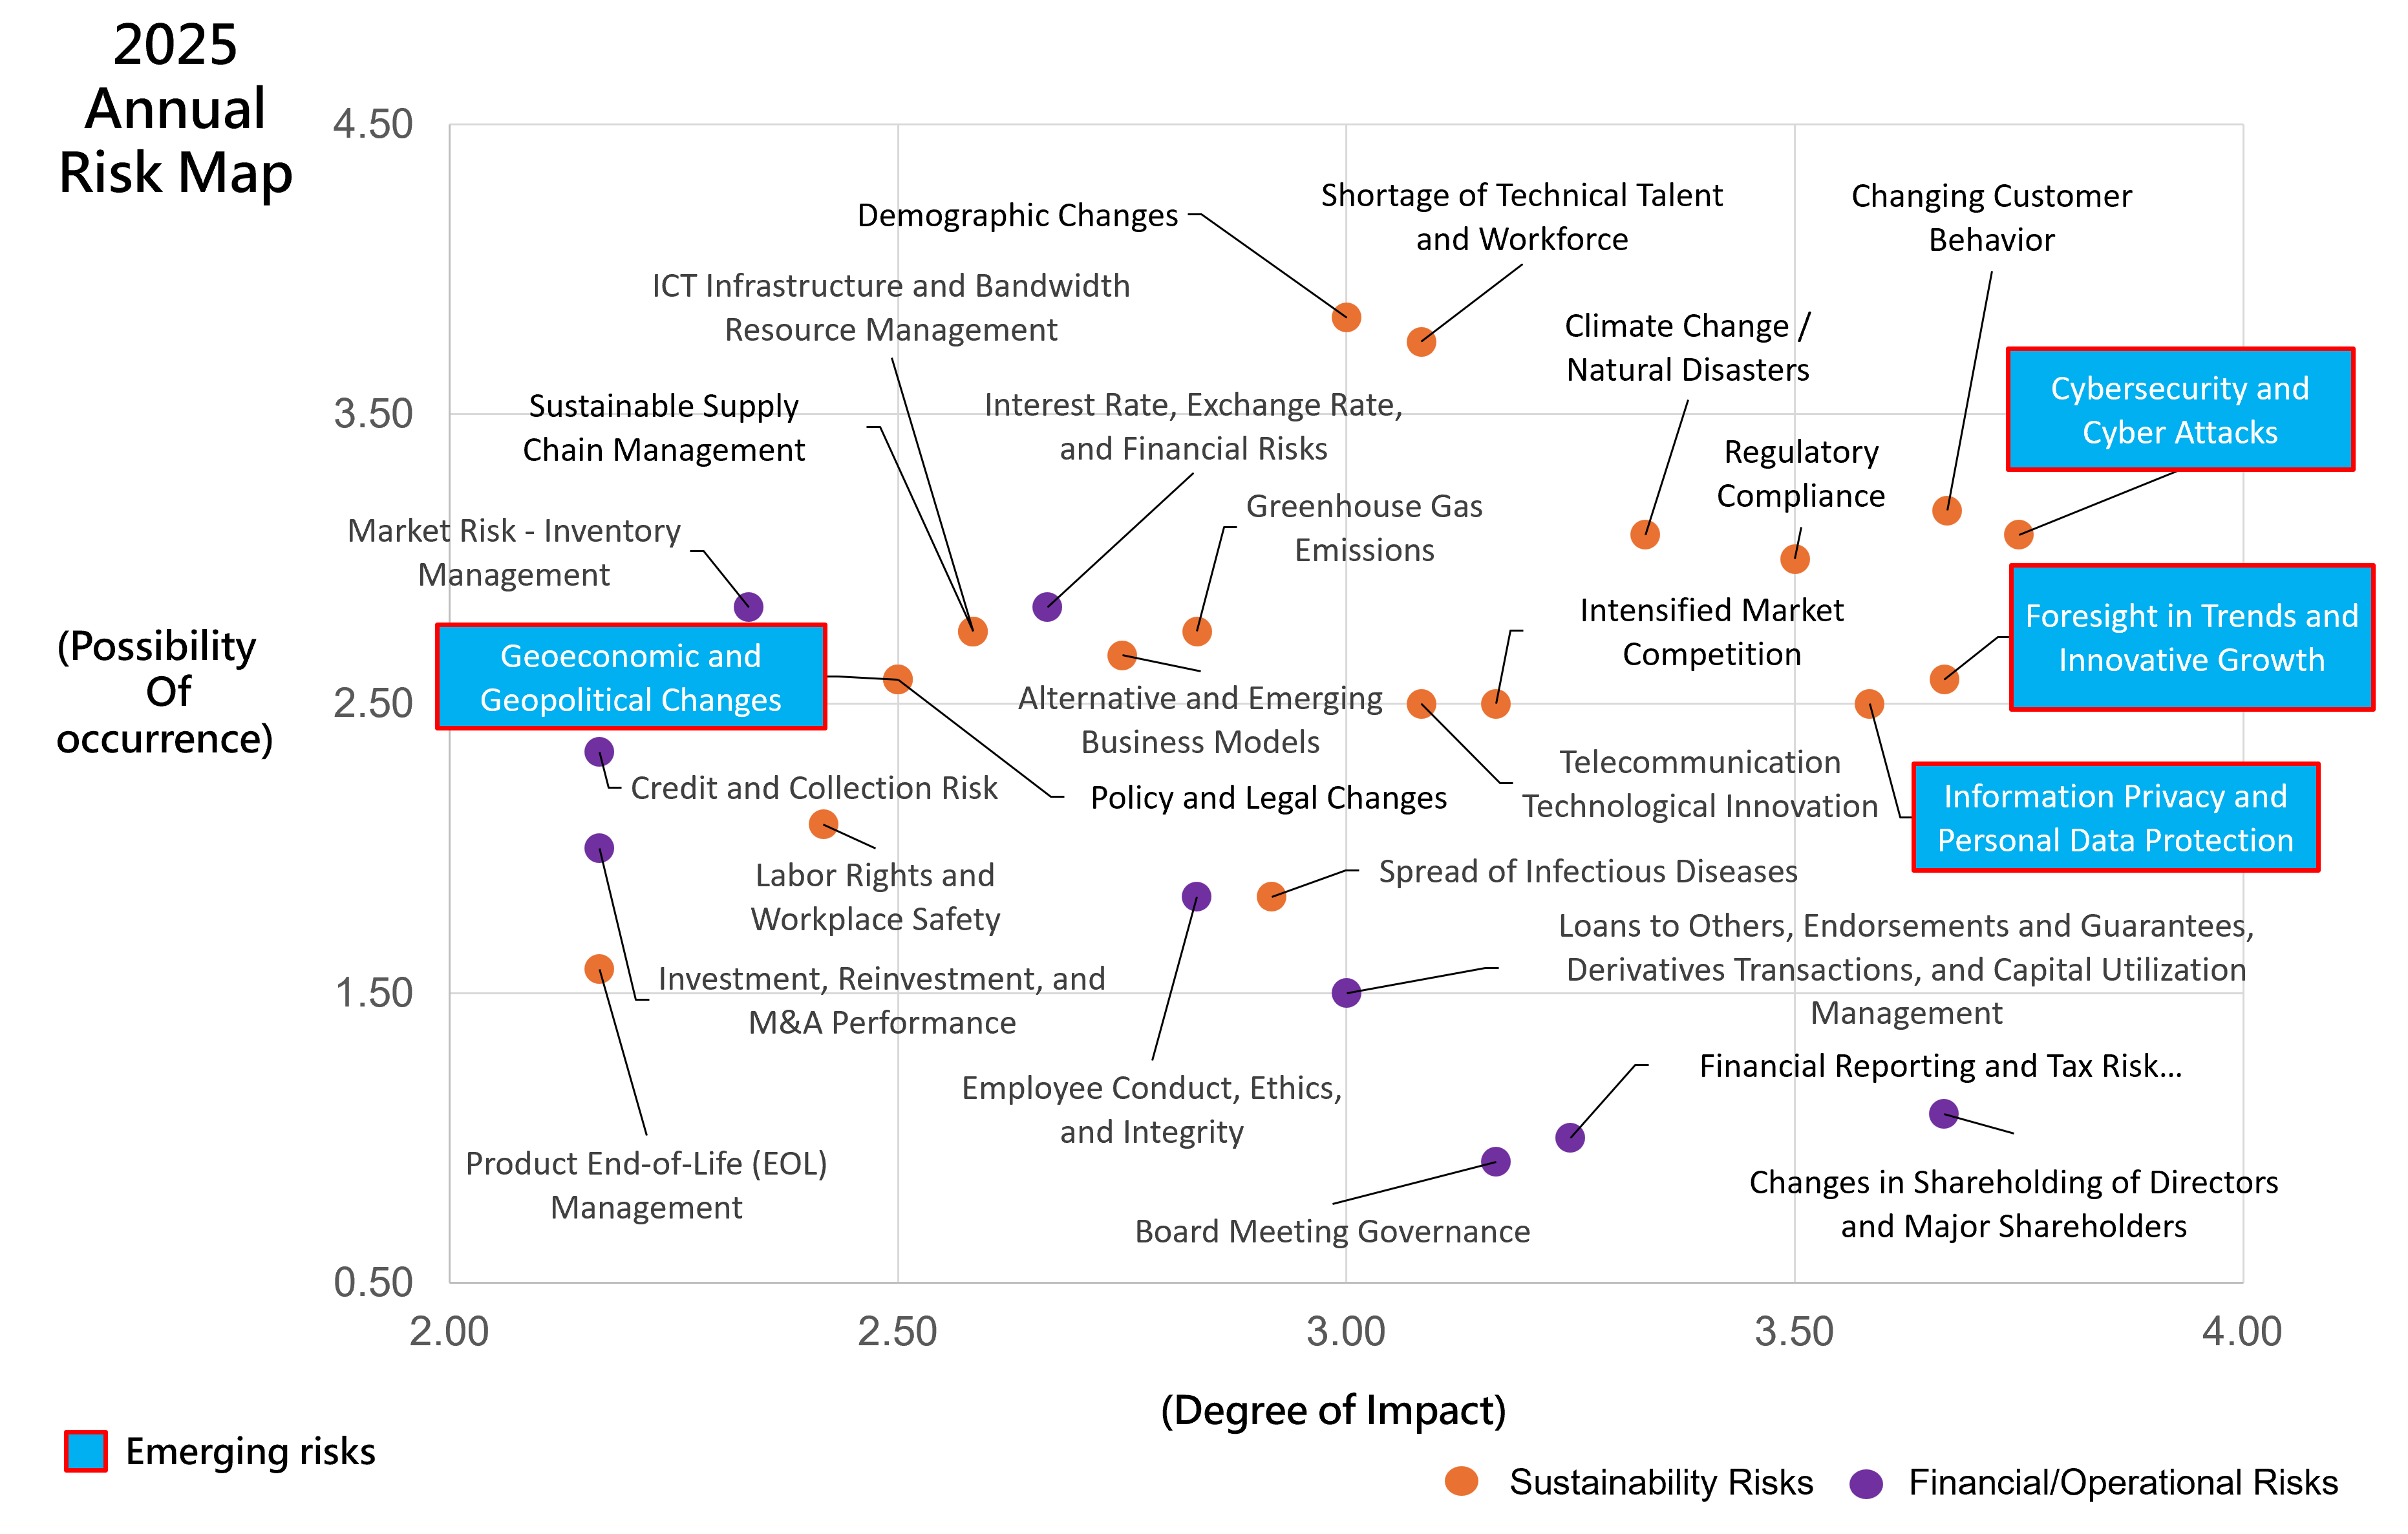
The Risk Management Steering Committee and
ESG working group reviews global, local, industrial trends, and
identifies relevant risks that are applicable to TWM on a corporate
level, discuss the risk prioritization according to the impact levels
and the possibility of occurrence.
Annually, an inventory is conducted based on the risk categories and
risk items, and each risk item is further reviewed to adjust the risk
description based on emerging international trends. After evaluating
potential impacts, each responsible unit shall select priorities
according to risk levels and adopt corresponding measures and actions to
control risks under acceptable range, and
corresponding measures and risk tolerance indicators shall be
formulated. Risk
Management Policy
Risk tolerance indicators, thresholds of overall gap between
target/metric and actual performance that the company is accepting to
tolerate, are established and monitored for each risk item. Taking
"Changes in customer behavior" and " Sustainable and Responsible Supply
Chain Management " as examples:
**Changes in customer behavior:**We Set the proportion of
"Double-Play" plan covers 80% of our existing own households client as
Risk tolerance Indicators
Sustainable and Responsible Supply Chain
Management:
Due diligence coverage of at least 90% of major Tier 1 suppliers.
Zero major supply chain disruptions.
Overall supply chain carbon emissions reduction of at least 9%.
Risk Management Matrix
Analysis of Emerging Risks and Opportunities
△ Emerging Risk:defined as an emerging and external risk that is
expected to have a significantly long-term impact on the company's
business.
Please Swipe
Left or Right View All.
Risk
Emerging Risk correlate with WEF category
TWM Material Topics
Description
Impact
Mitigating actions
Risk Tolerance
Information privacy and person data protection
Technological
Privacy protection
Domestic and international personal data privacy regulations are
becoming increasingly stringent, along with heightened public awareness
of personal data protection.
Data breaches involving personal information from emerging
services and products may lead to diminished user rights, reduced
company revenue, and damage to corporate reputation.
To establish a Personal Data Protection Commission and ensure the
protection of information privacy rights, as well as to promote the
rational use of personal data, the Executive Yuan has set up a
Preparatory Office for the Commission to strengthen oversight related to
information privacy and security. Our company must continuously invest
resources to establish a comprehensive personal data privacy management
system, in order to meet the external risks associated with compliance
with relevant laws and regulations and user expectations.
To provide a wide range of high-quality telecommunications and
value-added services, the scope of our innovative services and products
will continue to expand over the next three to five years. This will
involve the processing of a large volume of personal data and privacy
matters. In the event of an accidental personal data breach affecting
users' privacy, the company would be legally liable. For example,
compensation to affected users must be paid at not less than NTD500 and
up to NTD20,000 per person per incident, and in serious cases, an
administrative can fine between NTD150,000 and NTD15,000,000. In
addition to compensation to users, the company may also face impacts
such as user attrition and decreased revenue.
To address external impacts relating to information privacy and
information security, our company has established mechanisms for the
protection of users' personal data privacy, staying international trends
and regulatory requirements. In alignment with the development of
innovative services and products, we continuously optimize operational
processes involving personal data privacy.
By engaging impartial third-party assessments to verify the
effectiveness of our personal data privacy management, we ensure the
continued validity of certificates such as ISO 27001 and ISO 27701
(Information Security and Personal Information Management Systems), as
well as BS 10012 and ISO/IEC 29100 (Privacy Framework). These standards
are integrated into our business operations, driving ongoing
enhancements to our security mechanisms. We are planning the following
actions to further elevate our information privacy and security
standards:
Establishing and regularly updating information security policies
and standards.
Strengthening the functions of the dedicated information security
organization.
Continuously conducting personal data security audits and data
breach simulating drills.
Legal Disputes and Customer Complaint Controversies
Cyber Security and Cyber Attack
*
Technological
Information security
Cyberattack methods are rapidly evolving with the application of
AI and other advanced technologies, and the scope of attacks is
expanding to include both enterprises and their supply chains.
Regulatory authorities are strengthening information security
management for publicly listed companies and imposing increasingly
stringent network security protection requirements specifically for the
telecommunications industry.
Amid the emergence of various new cyberattacks across industries
worldwide, it is anticipated that, over the next three to five years,
hackers will strengthen their attack techniques by leveraging tools such
as AI. The company may be impacted by these emerging cyber threats, such
as ransomware attacks that encrypt corporate files, or social
engineering attacks that result in the leakage of sensitive information.
For example, if the company suffers a DDoS attack causing a one-day
service outage, the estimated revenue loss would be approximately 546
million NTD.
As a telecommunications critical infrastructure provider
designated by the Executive Yuan—and one of Taiwan's three major telecom
operators—any inability to withstand external cyberattacks could
severely disrupt user telecommunications services. This, in turn, may
lead to compensation for service interruptions, revenue reduction, and
reputational damage. Regulatory authorities have mandated the
strengthening and implementation of information security maintenance
programs, which means the company will need to continuously increase its
investment in defensive measures to mitigate external risks associated
with cyberattacks and regulatory compliance requirements.
To address external impacts related to cybersecurity, our company
must continuously invest resources to establish information and
communications security protection mechanisms and promote security
measures in order to comply with the regulatory authorities'
cybersecurity management requirements. We will review the effectiveness
of these protection mechanisms and the achievement of security
objectives, and report progress and benefits to the Information Security
and Personal Data Privacy Committee.
The cybersecurity protection mechanisms include:
Engaging external auditors to inspect and ensure compliance with
regulatory requirements, such as the Mobile Broadband Cybersecurity
Management directives from the Ministry of Digital Affairs.
Conducting penetration testing that simulates hacker behavior to
identify and remediate vulnerabilities.
Establishing various quantitative indicators to track the
security posture.
Enhancing the cybersecurity threat detection and management
mechanism (Security Operations Center, SOC) and conducting red team
exercises.
Monitoring and analyzing information security protection systems
and equipment, and evaluating the implementation of a Zero Trust
Architecture (ZTA) framework.
Information Security Incidents Handling
Geopolitical and Economic/Political Changes
*
Geopolitical
Supply chain management
Geopolitical Conflicts: Escalating regional conflicts and
international tensions could disrupt cross-border logistics and supply
chains.
Trade and Technology Controls:The scope of global
technology controls continues to expand amid growing emphasis on
technology sovereignty and supply chain autonomy.
Tariffs, export controls, and economic sanctions increase the risk of
sourcing critical equipment and components and create
greater uncertainty regarding their future
supply.
Supply Chain Concentration: Concentration of supply sources in
specific countries or regions may increase the risk of supply
disruptions and cost fluctuations.
Increased geopolitical volatility, coupled with greater
difficulty in controlling external factors, could lead to the following
operational impacts on Taiwan Mobile:
Supply Side: Delays or shortages of telecommunications equipment,
consumer electronics, and key components are possible.
Certain equipment may also be difficult to replace in the
short term.
Cost Side: Tariffs, transportation, and procurement costs may
rise.
Operational Side: Obstacles to equipment acquisition could affect
network construction, maintenance, and product sales. Over
the longer term, they may also affect supplier strategies and capital
expenditure planning.
Risk Monitoring: Continuously monitor changes in international
political and economic policies, trade policies, and supply
chains.
Risk Assessment: Incorporate country-, industry-, and
product-specific risks into supplier management.
Supply Resilience: Strengthen management of delivery times,
supply sources, and alternative solutions for high-risk suppliers and
product items.
Due diligence review coverage of at least 90% of major Tier 1
suppliers.
Zero major supply chain disruptions.
Responsiveness to the trend of innovation and creativity
energy
*
Technology innovation & application
The rapid evolution of cutting-edge technologies such as AI, 5G,
cloud computing, AIoT, and smart energy continues to reshape industry
competition and business models. Failure to promptly grasp technological
and market trends and transform existing core capabilities such as
networks, data, users, and channels into innovative services with market
value and scalable potential may result in missed opportunities in
emerging markets and growth. Furthermore, if investments in cutting-edge
technologies fail to effectively connect with market demand, business
models, and the company's core capabilities, uncertainties in resource
allocation and investment returns may arise. As AI is gradually scaled
up and implemented in operational and service scenarios, emerging risks
such as data governance, information security, privacy, AI ethics, and
legal compliance must also be considered.
Rapid changes in technology and the market may accelerate the
iteration of existing products, services and business models. If the
pace of innovation or commercialization is slower than the market, it
may affect new growth momentum and competitive advantage. If investments
in new technologies and AI infrastructure fail to achieve economies of
scale, it may affect resource allocation and return on investment. If AI
applications do not properly manage data, cybersecurity, ethical and
legal compliance risks, it may also affect operational resilience,
customer trust and corporate reputation.
TWM continues to leverage our multi-tiered growth strategy of
Telco, Telco+, and Telco+Tech to seize opportunities in AI and
cutting-edge technology development. We will combine our core
capabilities—including millions of users, networks, data, and
distribution channels—to develop differentiated and scalable products
and services. We will strengthen our market orientation and investment
discipline, dynamically reviewing technology maturity, market demand,
and investment returns through PoC, MVP, and phased commercial
validation mechanisms. We will deepen our AI infrastructure, models,
applications, and governance capabilities, while ensuring data security,
privacy, ethics, transparency, and legal compliance. We will integrate
CT, IT, OT, AI, and IoT, expanding enterprise solutions and emerging
markets through strategic alliances and cross-industry collaborations.
Furthermore, we will utilize AI to improve operational, network, and
energy efficiency, strengthening our resilience and sustainable
competitiveness, and creating long-term value for shareholders,
customers, employees, and society.
User Growth & Revenue Performance
Number of Projects and Participants
Risk Culture
Regular risk management education for all non-executive
directors
In accordance with Article 40 of《Corporate Governance Best Practice
Principles》, the Company requires directors to complete at least three
hours of risk management training annually to enhance their relevant
capabilities. Training programs for directors please reference the
company annual report P.41. Annual
report
Focused training throughout the organization on risk
management principles
In order to fortify risk response competency of employees and cultivate
risk management culture, we conduct risk management trainings every year
with topics such as how to conduct risk management and information
security. We also test employees with simulated phishing attacks. Such
trainings and simulation sessions aim to enhance awareness of employees
and train them to respond effectively in accordance with Company's
regulations. Consequently, creating risk management culture within the
company is a responsibility for all employees, ensuring sustainable
business operations. In 2023, the total number of hours for the risk
management course is 78,032.6 hours. In 2024, the total number of hours
for the risk management related courses is 96903.8 hours. In 2025, the total number of hours for the risk management related courses is 137,136.55 hours.
New employee orientation programs include risk management, such as
code of conduct, information security training, labor safety and health,
and prevention of discrimination and harassment. These programs aim to
enable new employees to understand our company culture and our stand on
risk.
Financial incentives which incorporate risk management
metrics
Employees are encouraged to propose suggestions on how to lower risks
and improve the performance and quality of their work while achieving
objectives. Awards will be given to employees in recognition for
suggestions deemed valuable to the company, and these credits will be
noted in their evaluation. Employees with better performance will
receive higher bonus and salary increase. On the contrary, if an
employee violates the regulations of internal control system or
information security policy, the employee may be recorded a warning, and
may not receive a rewarding performance evaluation. The poor performance
ranking will lead to a lower bonus and salary adjustment.
Incorporation of risk criteria in the development of products
and services
As a telecommunications provider of critical infrastructure, Taiwan
Mobile fully recognizes that the stability and security of IT systems
are of utmost importance. Accordingly, in the development and
maintenance of our information systems, we not only adhere strictly to
security standards but also regard risk assessment as a core element.
From requirements planning to daily operations, every stage incorporates
comprehensive risk assessments to ensure system stability, availability,
and information security, thereby reducing the potential impact of
system disruptions or data breaches on our customers and operations. In
the development of our IT products and services, we primarily conduct
risk assessments across three dimensions: technical architecture and
systems, system performance and availability, and information security
and privacy.
1. Technical Architecture and Systems Assessment
We focus on ensuring that the system's foundational design is robust
and sustainable, preventing architectural issues that could hinder
future scalability and maintenance.
Key Areas of Assessment:
Scalability Risk: Evaluating whether the system design has
sufficient flexibility to accommodate future business growth and new
feature integration. We commonly adopt microservices or modular designs,
enabling independent development and scaling of services while reducing
interdependencies.
Technology Selection Risk: Assessing the maturity of selected
technologies and the extent of community support. We also avoid
over-reliance on a single vendor (Vendor Lock-in) to ensure that
replacement or integration in the future does not result in excessive
costs or technical barriers.
Compatibility Risk: Evaluating the stability of integrations
between new systems, legacy systems, third-party services, or APIs. This
includes integration testing and the establishment of standardized API
interfaces to reduce risks caused by version updates or interface
changes.
2. System Performance and Availability Assessment
We ensure that systems can withstand high traffic loads and maintain
service stability even under unexpected conditions, thereby delivering a
high-quality user experience.
Key Areas of Assessment:
Capacity and Performance Risk: Using stress testing and load
testing to simulate peak traffic conditions, ensuring systems remain
stable and response times stay within acceptable limits.
High Availability Risk: Preventing single points of failure by
adopting redundant designs, such as multi-data center or multi-cloud
deployments, with automated failover mechanisms to seamlessly switch to
backup systems when primary systems encounter issues.
Disaster Recovery (DR) Risk: Establishing detailed disaster
recovery plans, including regular backups and offsite redundancy. We
also define clear Recovery Time Objectives (RTO) and Recovery Point
Objectives (RPO) to ensure rapid service restoration and minimal data
loss in the event of a disaster.
3. Information Security and Privacy Risk Assessment
This is the most critical dimension in our development process, aimed
at safeguarding both customer and corporate data while ensuring
compliance with international security standards.
Key Areas of Assessment:
Secure Development Lifecycle: Incorporating ISO 27001:2022 and
related international standards throughout development, testing, and
deployment to uphold confidentiality, integrity, and availability (CIA
principles) from the outset.
Secure System Design: Embedding security architecture in early
design stages. For instance, identity authentication and access control
follow the principle of least privilege, granting users only the minimum
level of access necessary.
Pre-Deployment and Operational Security Testing: Conducting code
reviews, penetration testing, and vulnerability scans before system
launch to eliminate potential threats. Post-deployment, we maintain
continuous monitoring, timely updates, and regular reviews to ensure the
effectiveness of security measures.
Supply Chain Risk Management: Requiring third-party vendors to
comply with international standards (such as 3GPP, ITU, NIST) and
provide relevant certifications, thereby reducing risks arising from the
software supply chain.
Through these three dimensions of risk assessment, we ensure that our
IT products and services not only meet functional requirements but also
deliver a stable, efficient, and secure user experience.